PROOF, NOT PROBABILITY.
AI Accelerates Code. Risk Remains. Prove It’s Safe.

Proven Software Assurance for C, C++, and Rust
Detects 100% of memory‑safety issues and runtime errors - or proves their absence - in C, C++, and Rust code, with AI‑assisted automation.

Guarantee
Sound and exhaustive analysis, zero false negatives. Explore all possible execution paths and input values.

Efficiency
Focus on real issues with near-zero false positives and precise root-cause analysis. AI automates up to 90% of the setup.

Fits Your Pipeline
CI/CD ready, target HW emulation, no target HW needed - drop it into your existing workflow with minimal setup.

Go Beyond Traditional Software Verification
Traditional Static Analysis
Fast and scalable, but heuristic approaches lack full path- and context-sensitivity, which can miss deep bugs and generate false positives.
Dynamic Testing
Finds real defects, but only in the paths and inputs actually executed, and some issues remain silent.
AI-Native Analysis
Accelerates analysis and remediation, but results remain probabilistic and require validation.
TrustInSoft
Exhaustive analysis delivers verified proof, not probability, of what can and cannot happen.
The TrustInSoft Difference
Find more bugs, backed by a guarantee no other approach provides – turning memory-safety and runtime-error verification into a measurable, repeatable industrial process for your team.

Controlled Risk
Reduced field support costs. Avoid the bugs behind critical cyberattacks, lowering brand and litigation exposure. Streamlined certification and customer validation.

Operational Efficiency
Early detection and easy remediation. Near-zero false positives cut triage time. Reduced coverage and target-hardware testing costs.

Built for the AI Era
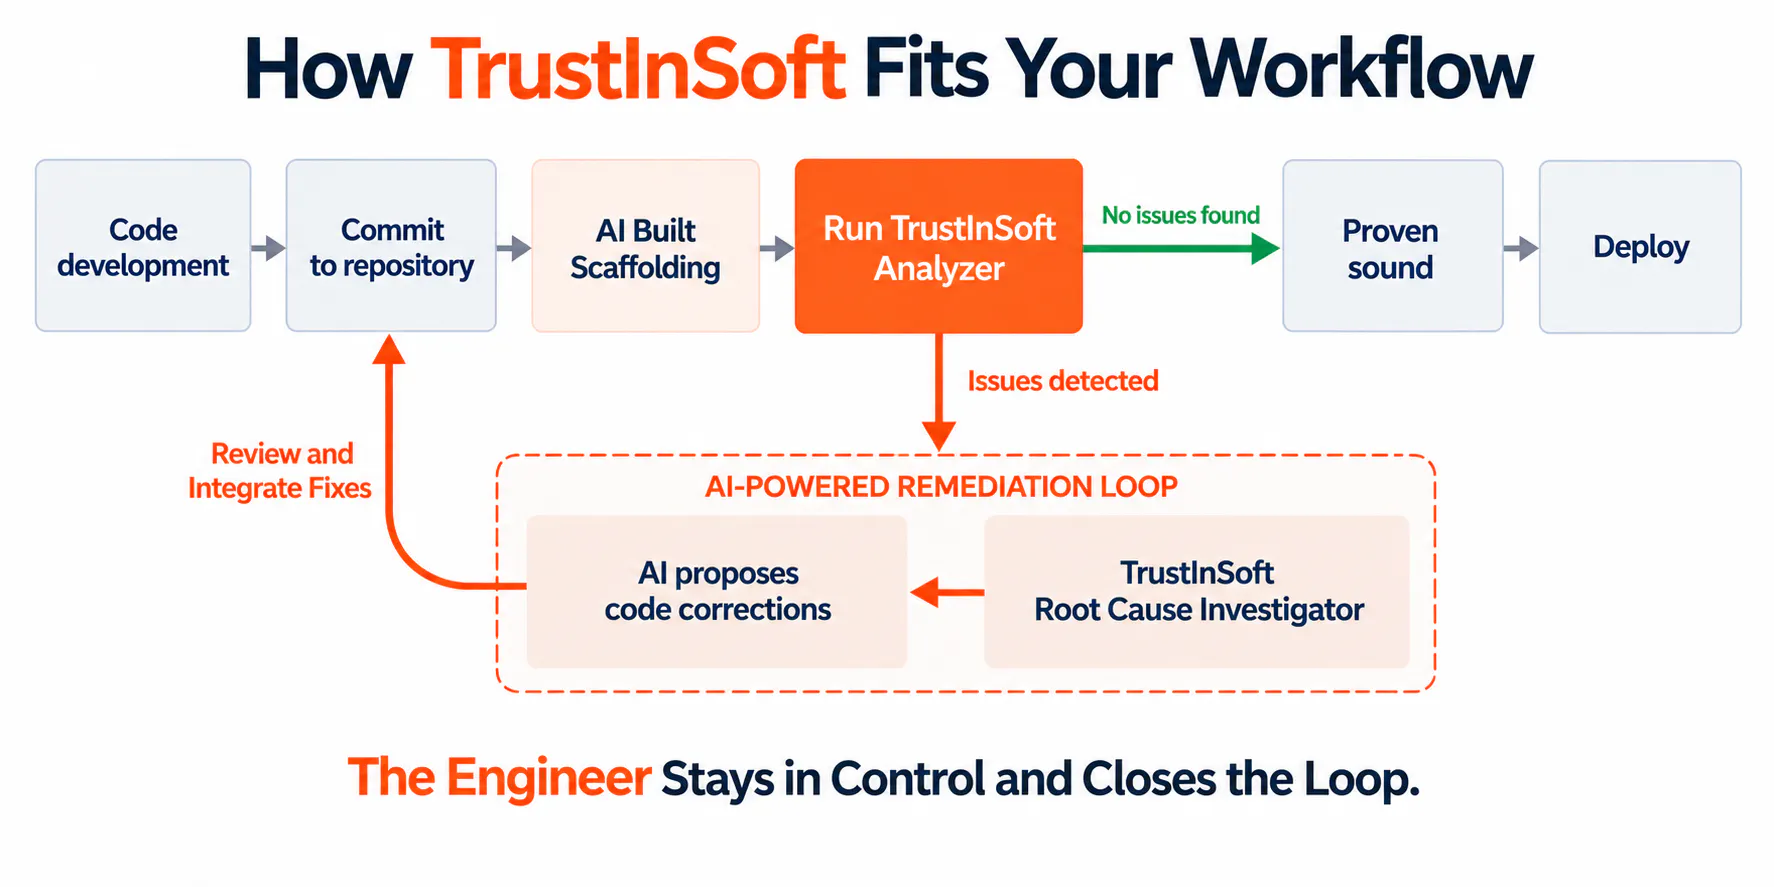
Deterministic checks on AI-generated code. AI automates up to 90% of the verification setup. Engineers stay in control of intent and results.